Product Security
Securing a RAG chatbot before it speaks for you
A chatbot that represents your thinking is not only a product feature. It is a public security boundary, a cost center and a reputational surface.
Written by
David Davila
September 19, 2026
A chatbot is more than you would expect
The first mistake is treating a RAG chatbot as a friendly input box with a model behind it. That framing is too simplistic, too small. A chatbot that answers on behalf of a person or a company is a public channel, a running cost and a trust vehicle at the same time.
Ask David looks simple from the outside: a visitor asks a question and gets a contextual answer. Underneath, the system touches a LLM model, persistent relational database, cloud infrastructure, vector database, session memory, logs, user data and a curated knowledge base (KB). Every one of those layers can fail in a different way, so it's important to understand the associated risks before launching one.
Reputation: The bot speaks with your tone
When a chatbot answers in first person, users do not experience it as a neutral system. They experience it as a proxy for the person or brand. If it invents, leaks internal details, responds to manipulation or sounds careless, the reputational damage is immediate.
That is why the Ask David pipeline separates visitor memory from the knowledge base. Memory can help understand the visitor's context, but claims about David must come from retrieved, curated content. The chatbot should be helpful, but it should also know when to say that it does not have enough context.
Technical Risk: Prompt injection is the obvious one to look out for
Prompt injection is when a user tries to override the system's instructions from inside the conversation. It can be direct, like asking the model to ignore previous rules, or indirect, like asking it to reveal hidden prompts, keys, retrieved chunks or internal configuration.
The mitigation is not one magic prompt. It is a set of boundaries: server-side secrets, trusted and untrusted prompt sections, input length limits, no knowledge base mutation from user messages, no internal metadata returned to the browser, and clear instructions that user text and session memory are content rather than authority.
Retrieval Risk: Bad context produces confident answers
RAG changes the security problem because the model is no longer answering from a prompt alone. It is answering from retrieved material. If the knowledge base is polluted, messy, poorly chunked or too permissive, the assistant can sound confident while grounding itself in the wrong evidence.
For Ask David, that makes corpus governance part of security. Production knowledge lives in curated Markdown files built from transcribed interviews. User messages do not write back into the KB, retrieval uses score thresholds, and fallback is allowed when the retrieved context is weak. The goal is not to force an answer. The goal is to make uncertainty visible before it becomes a false claim.
Economic Risk: Every question has a cost
A public AI endpoint can become a small open wallet if it is left unprotected. Even when each answer is cheap, repeated bot traffic, long prompts, automated sessions or failed retrieval loops can turn into real costs.
That is why the Ask David implementation combines rate limiting, Turnstile human verification before the first AI call, a three-question Guest limit, and structured logs for tokens, latency, model usage and estimated cost. Security here is not only about preventing leaks. It is also about keeping usage within budget.
Data Risk: Logs are both useful and sensitive
Logs are essential for observability. They show which questions users ask, which chunks were retrieved, which models were used, how many tokens were consumed and whether answers fell back. Without logs, the product cannot improve responsibly.
But logs also collect user-provided context: name, email, company and session memory. That means they need intentional schema design, server-side access only, no accidental frontend exposure, and a clear reason for every field stored. Good observability should not become quiet over-collection. Basically, information just in time.
Privacy Risk: Trust starts before the first answer
Security is not only about stopping attackers. It is also about being honest with normal users. A chatbot that collects questions, contact details, company context and analytics signals needs clear privacy boundaries before the interaction becomes useful enough for people to share sensitive information.
That means delaying unnecessary data collection, explaining what is stored, asking for contact details only when there is enough conversational context, and separating site performance measurement from advertising. In a European context, consent for optional analytics is not cosmetic. It is part of the product specs.
Good practices for a RAG like Ask David
The practical checklist is simple but important: keep API keys server-side, validate and truncate user input, require human verification before model calls, rate limit requests, separate trusted KB from untrusted memory, avoid returning retrieval internals to the client, and log enough to monitor quality and cost.
Then add the less glamorous controls: review KB changes, set retrieval thresholds, keep fallback responses acceptable, define retention rules, collect optional analytics only with consent, and make sure the privacy notice matches what the system actually stores.
The other important practice is humility. A RAG system is not made safe once. It is monitored, tested and revised. Every new feature, memory rule, data field, consent flow or model upgrade can change the threat model.
The Open Edge
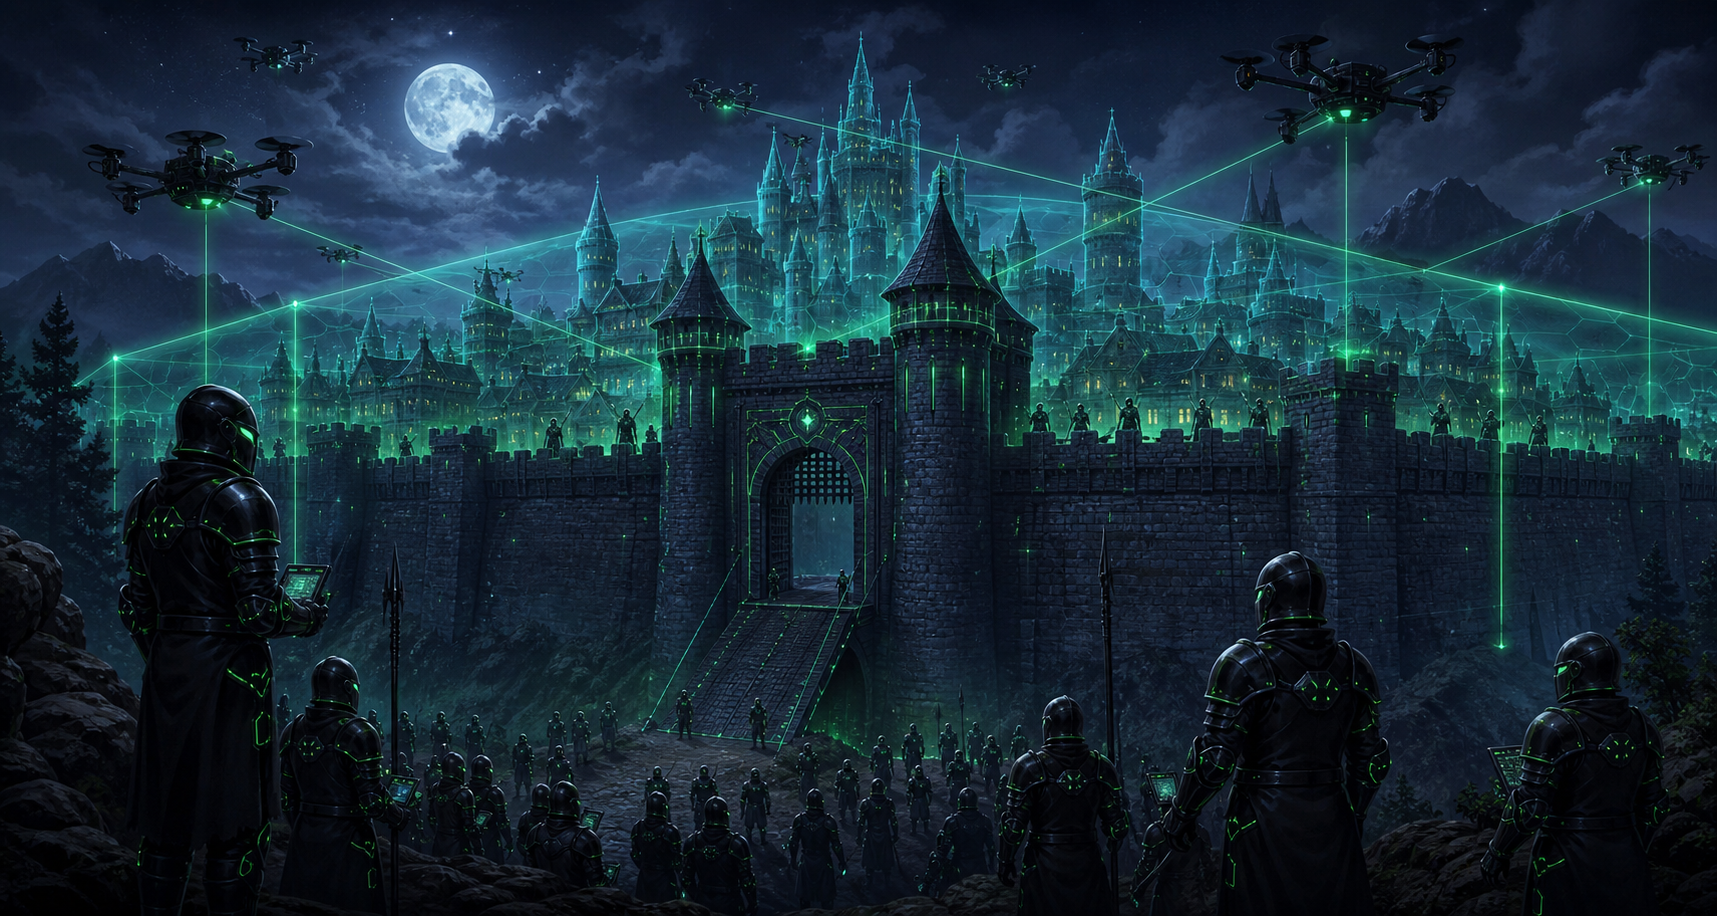
The uncomfortable part is that the threat model is not finished. New model capabilities, new automation tools, new jailbreak patterns and new ways to chain services together will keep producing attack shapes that are hard to name today. A secure chatbot is not a locked castle. It is a defended city that keeps watching the horizon.
Written by David Davila
About the author
David Dávila Arimuya is a product leader and founder of P&G Partners, focused on product strategy for Cloud, AI and B2B2C companies.